
What Makes Codex Security Omit a SAST Report
This article explains why Codex Security diverges from traditional SAST tools. While classic scanners rely on pattern matching and generate noisy, often false positives, Codex Security uses AI-driven constraint reasoning to trace data flows, validate exploitability end to end, and report only reachable vulnerabilities. The result is fewer false alerts, faster triage, and better remediation, ideally layered alongside traditional SAST in CI pipelines.
If you work in application security or you're simply curious about how modern AI tools hunt for software vulnerabilities, this article is for you. Below, we'll walk through why Codex Security takes a different path from classic Static Application Security Testing (SAST), how AI-driven constraint reasoning changes the game, and why this approach tends to produce fewer false positives than the scanners most teams grew up with.
The Problem With Traditional SAST
Traditional SAST tools scan source code line by line, matching patterns against known vulnerability signatures. If the code looks like something from a database of dangerous patterns—a SQL query built from user input, for example—the tool raises an alert.
This approach has kept security teams busy for two decades, but it comes with well-known drawbacks:
- Data-flow blindness at scale. SAST tools flag anything that could be dangerous, even when the surrounding logic makes exploitation impossible.
- Alert fatigue. Many teams report that a large share of findings are noise. When nearly every scan floods engineers with issues that don't matter, real vulnerabilities get lost in the shuffle.
- No understanding of intent. Pattern matching cannot answer the question a security reviewer actually cares about: can this code path actually be reached with attacker-controlled data?
The result is a trade-off teams know too well: turn the sensitivity up and drown in false positives, or turn it down and risk missing genuine bugs.
How Codex Security Thinks Differently
Codex Security replaces brute-force pattern matching with reasoning. Instead of asking "does this code resemble a known bad pattern?", it asks "given the constraints of this program, is this vulnerability actually exploitable?"
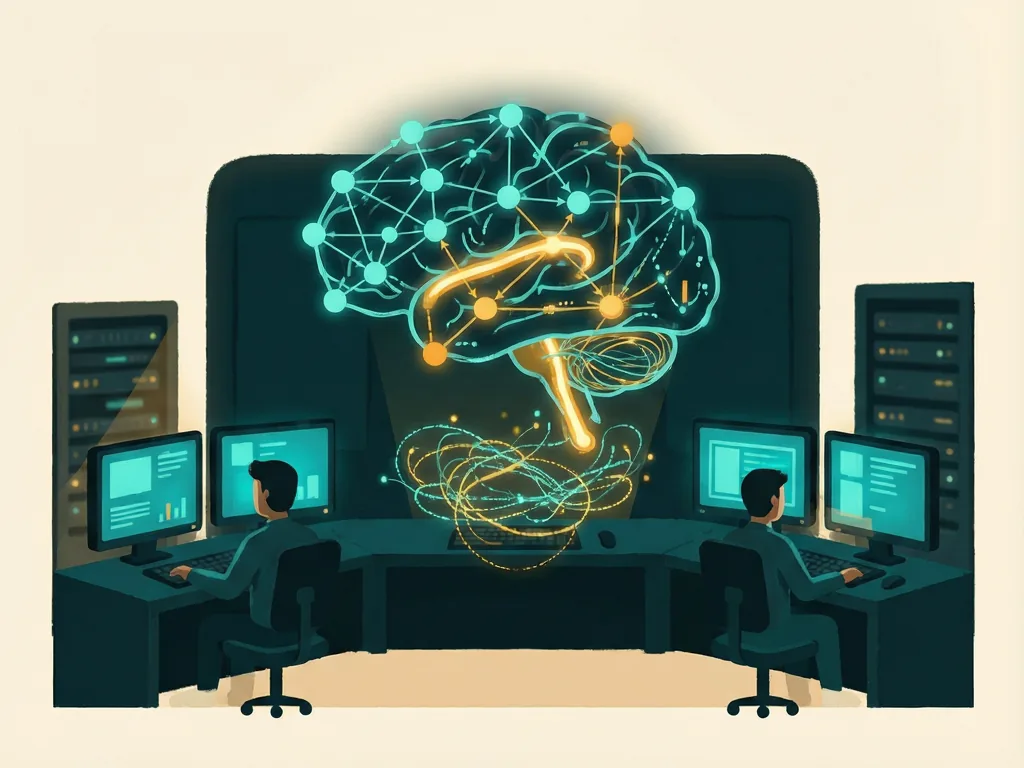
That's what AI-driven constraint reasoning means in practice. The model builds an understanding of what the code is supposed to do, traces how data moves through the application, and evaluates the conditions that would need to be true for a vulnerability to exist. It then validates those conditions against the actual codebase before reporting anything.
This validation step is the key differentiator. A finding only survives if the AI can demonstrate the vulnerable path end to end. Suspicious-looking code that is guarded elsewhere, sanitized properly, or simply unreachable doesn't make the cut.
Fewer False Positives, More Trustworthy Results
Because every finding is reasoned about and validated rather than pattern-matched, the signal-to-noise ratio changes fundamentally. A report from an AI-driven approach like Codex Security is more likely to describe a genuine, reachable issue with context explaining why it matters.
That shift has practical consequences for engineering teams:
- Developers stop ignoring the scanner. When alerts reliably point at real problems, teams engage with the results instead of dismissing them.
- Triage time shrinks. Security engineers spend their hours investigating confirmed risks rather than debunking phantom ones.
- Remediation moves faster. Findings arrive with reasoning attached, which makes it easier to understand the bug and fix it correctly on the first try.
Where the Two Approaches Fit
None of this means traditional SAST is worthless. Signature-based scanning is fast, cheap, deterministic, and works well as a first-pass filter in CI pipelines. The AI-driven approach shines where SAST struggles: complex codebases with many layers of indirection, nuanced business logic that determines exploitability, and situations where the cost of chasing false positives outweighs the cost of deeper analysis.
In practice, many mature security programs will end up layering the two—using conventional tools for broad, rapid coverage and AI reasoning for depth and precision where it counts.
One honest caveat: AI-driven analysis is newer, and its behavior is less transparent than a deterministic rule set. Teams adopting it should validate results on their own codebases, keep humans in the loop for critical decisions, and treat the AI's explanations as a starting point for review rather than a final verdict.
The Bigger Picture
Codex Security's approach reflects a broader shift in security tooling: from asking "does the code match a bad pattern?" to asking "can an attacker actually cause harm here?" Constraint reasoning and validation move the industry closer to findings that engineers trust and act on. For teams exhausted by noisy scanners, that change alone is worth paying attention to.
As AI models get better at understanding program intent, expect the gap between pattern-matching tools and reasoning-based tools to grow. Codex Security is an early, concrete example of what that next generation looks like—and why fewer false positives may be its most important selling point.
Comments (0)